Cybersecurity Checklist: Manufacturing IT Services
Manufacturing IT systems support modern manufacturing margins which depend on continuous uptime in Operational Technology (OT) and on the integrity of Information Technology (IT) systems, especially the Enterprise Resource Planning (ERP) platform. Unplanned downtime directly creates unfavorable labor efficiency variances and material under-absorption of fixed manufacturing overheads; it can also compromise bill of materials (BOM)…
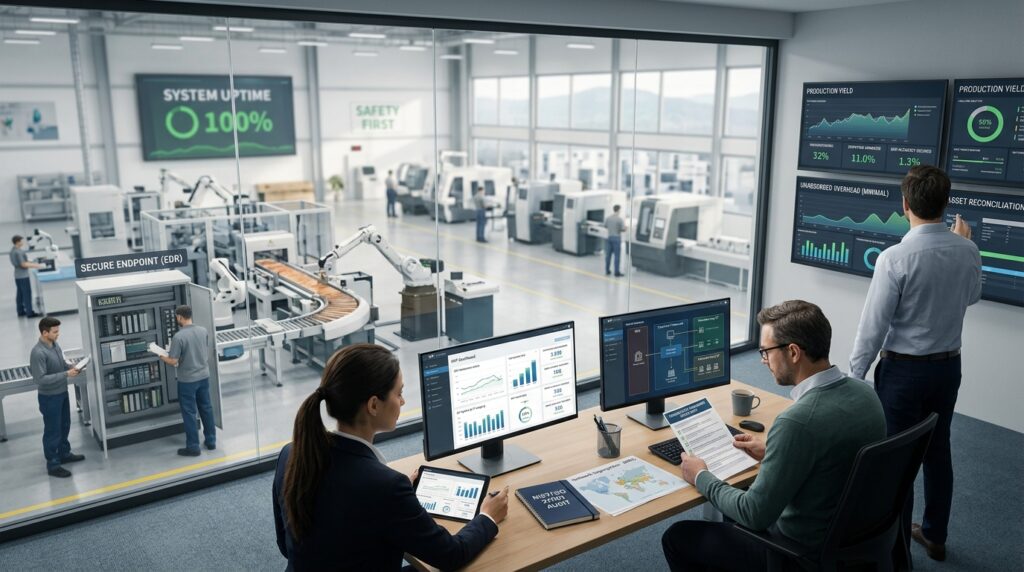
Manufacturing IT systems support modern manufacturing margins which depend on continuous uptime in Operational Technology (OT) and on the integrity of Information Technology (IT) systems, especially the Enterprise Resource Planning (ERP) platform. Unplanned downtime directly creates unfavorable labor efficiency variances and material under-absorption of fixed manufacturing overheads; it can also compromise bill of materials (BOM) accuracy. The controls below tie cybersecurity to physical plant workflows and the integrity of internal controls over financial reporting (ICFR).
Prerequisites
Complete Asset Inventory List Tied to the Fixed Asset Register
Start with a floor-to-book reconciliation. You must have a complete log of all internet-connected devices (servers, PLCs, SCADA systems, IIoT sensors) mapped against your Fixed Asset Register (FAR).
- Action: Identify “ghost assets” on the factory floor that bypass IT governance but remain on the depreciation schedule.
Regulatory and Compliance Frameworks (ITGC)
Adopt NIST SP 800-82 or ISO/IEC 27001 as the benchmark for your IT General Controls (ITGC). This supports external financial audits, particularly for SOX compliance, and can help when securing favorable terms for Cyber Liability Insurance.
Dedicated Manufacturing IT Services Partner or Team
Determine whether to utilize internal headcount or outsource to a Managed Service Provider (MSP).
- Financial Control: Ensure MSP contracts include strict Service Level Agreements (SLAs) with financial penalty clauses for failing to meet Recovery Time Objectives (RTO) during month-end close operations.
Network Assessment Tools
Deploy software to baseline network traffic.
- Accounting Treatment: Evaluate these tools under ASC 350-40 (Internal-Use Software) to correctly capitalize implementation and configuration costs versus expensing ongoing SaaS subscription fees as operating expenses (OpEx).
Step 1: Evaluating the Current Security Posture
Mapping IT and OT Networks
Identify every bridge between the corporate network and the production floor, including the general ledger and systems that handle payroll or accounts payable. A breached OT network can allow lateral movement into financial sub-ledgers. From there, procurement fraud or manipulation of supplier bank details becomes a realistic risk.
Identifying Legacy System Vulnerabilities
Assess older manufacturing equipment running unsupported operating systems (e.g., Windows XP on legacy aluminum die-casting machines).
- Risk: These machines cannot accept modern security patches. Determine if the cyber risk necessitates accelerating depreciation or taking an impairment charge under ASC 360 to replace the asset early.
Assessing Current Access Controls (Segregation of Duties)
Review administrative access matrices. Ensure strict Segregation of Duties (SoD) between personnel who can alter BOM routings in the ERP and those who approve standard cost updates. Remote access portals used by third-party maintenance vendors must be limited to approved accounts and monitored sessions.
2: Implementing the Cybersecurity Controls
Establishing Network Segmentation (DMZs)
Implement firewalls and demilitarized zones (DMZs) to physically and logically separate corporate IT from manufacturing OT.
- Workflow Impact: If the corporate network is hit by ransomware, the production floor must still be able to pull raw materials under FIFO/LIFO rules and execute work orders offline. Otherwise, a corporate IT incident can shut down the plant and reduce margin.
Enforcing Identity and Access Management (IAM)
Deploy Role-Based Access Control (RBAC) and Multi-Factor Authentication (MFA).
- Audit Trail: This enforces accountability for shop-floor workflows. Only authorized shift supervisors should be able to execute standard cost overrides or post adjustments related to cycle counts and scrap write-offs in the system.
Deploying Endpoint Detection and Response (EDR)
Install EDR agents or sensors on all compatible endpoints. Model the ongoing subscription costs in the annual IT OpEx budget, then absorb the cost through manufacturing overhead allocations where appropriate.
Formulating a Data Backup and Incident Response Plan
Establish immutable backups for critical machine configurations and ERP databases. Test restores against the month-end close timetable; do not assume backups are recoverable.
Realistic Scenario: Discrete Manufacturing Cyber Incident
Context: A $40M turnover lawnmower and woodfire manufacturer (utilizing aluminum casting operations).
The Event: A floor supervisor plugs an infected USB drive into a legacy Windows XP SCADA terminal controlling an aluminum casting furnace. Ransomware locks the local OT subnet. Because the IT/OT networks lacked proper segmentation, the malware attempts to encrypt the primary ERP server containing standard costing and inventory modules.
Financial Impact Matrix (48-Hour Downtime):
| Cost Category | Financial Impact / Calculation | Amount |
|---|---|---|
| Direct Materials (Scrap) | 2,500 lbs of molten aluminum ruined in process, plus refractory damage. Written off at standard material cost. | $14,500 |
| Labor Efficiency Variance | 45 line workers idle for 2 shifts (45 workers x 16 hours x $28/hr fully burdened). | $20,160 |
| Unabsorbed Overhead | Fixed factory overhead unallocated to units produced during the 48-hour window. | $32,000 |
| Expedited Freight | Upgrading LTL shipments to dedicated air freight to meet SLA penalties with major wholesale distributors. | $18,500 |
| Total Gross Margin Hit | Direct reduction to EBITDA from a single unsegmented OT breach. | $85,160 |
Practical Shortcut Used: The financial controller had previously enforced strict ITGCs, so the ERP database had a 4-hour Recovery Point Objective (RPO) backup to an immutable cloud vault. The company did not need to pay the ransom or rebuild weeks of data. The accounting team spun up a virtual ERP instance and used offline cycle counting sheets maintained by warehouse staff to bridge the 4-hour inventory gap, closing the month on Day 5 without audit qualifications.
Common Control Failures to Avoid
Treating IT and OT Security as the Same Thing
Applying automated Microsoft security patches to OT equipment (PLCs) without sandboxing or testing. This can reboot production machinery mid-cycle, causing tool crashes, ruining WIP, and driving significant unabsorbed manufacturing overhead due to unplanned downtime.
Neglecting Employee Awareness Training
Failing to train floor workers on physical security. Phishing is not limited to office staff; floor managers accessing supplier portals via shared shop-floor workstations are common sources of credential harvesting.
Ignoring Cycle Counting Controls During System Downtime
Assuming inventory is accurate post-breach. If automated barcode scanners go down, floor staff often resort to manual workarounds. Failure to perform an immediate spot stocktake upon system restoration leads to severe inventory valuation errors and phantom stock at month-end.
Steady State: Securing and Maintaining the Environment
Continuous Monitoring and Threat Hunting
Continuous network monitoring identifies issues before they interrupt physical plant workflows. It also reduces downtime costs from repeated system reboots and machine reprogramming.
Routine Audits and Penetration Testing
Penetration testing should be scheduled and evidenced as part of the control cycle rather than handled as an occasional exercise. External auditors will expect proof that internal controls and risk management frameworks are working. Regular testing also validates that access matrices align with delegated financial authorities.
Achieving Stable, Secure Production
In a hardened environment, absorption costing models are less likely to be distorted by cyber downtime. Production data and yield reporting remain more reliable. The finance team can produce reliable forecasts for the P&L, Balance Sheet, and cash flow without building in arbitrary reserves for cyber-related business interruptions.
Executive FAQs
Why are specialized Manufacturing IT Services necessary?
Corporate IT generally prioritizes data confidentiality. In manufacturing, machine availability often comes first. Standard IT protocols may shut down a compromised port immediately. On a factory floor, shutting down a network port mid-batch on a continuous process line (like fabric knitting or aluminum casting) destroys WIP and damages tooling. Specialized MSPs isolate threats while allowing machinery to safely cycle down.
How do we budget for continuous cybersecurity updates?
Treat cybersecurity as recurring IT overhead rather than a one-time CapEx project. Model it into your annual operating budget as a fixed IT overhead. When negotiating supplier contracts, use your documented cybersecurity controls as evidence of supply chain reliability to demand better payment terms (e.g., pushing net 30 to net 60).
Can network segmentation completely prevent a ransomware attack?
No. It limits the scope of compromise. If the corporate email server is compromised, segmentation helps prevent the attack from traversing into the PLCs controlling the factory floor, protecting manufacturing yields and standard cost allocations.